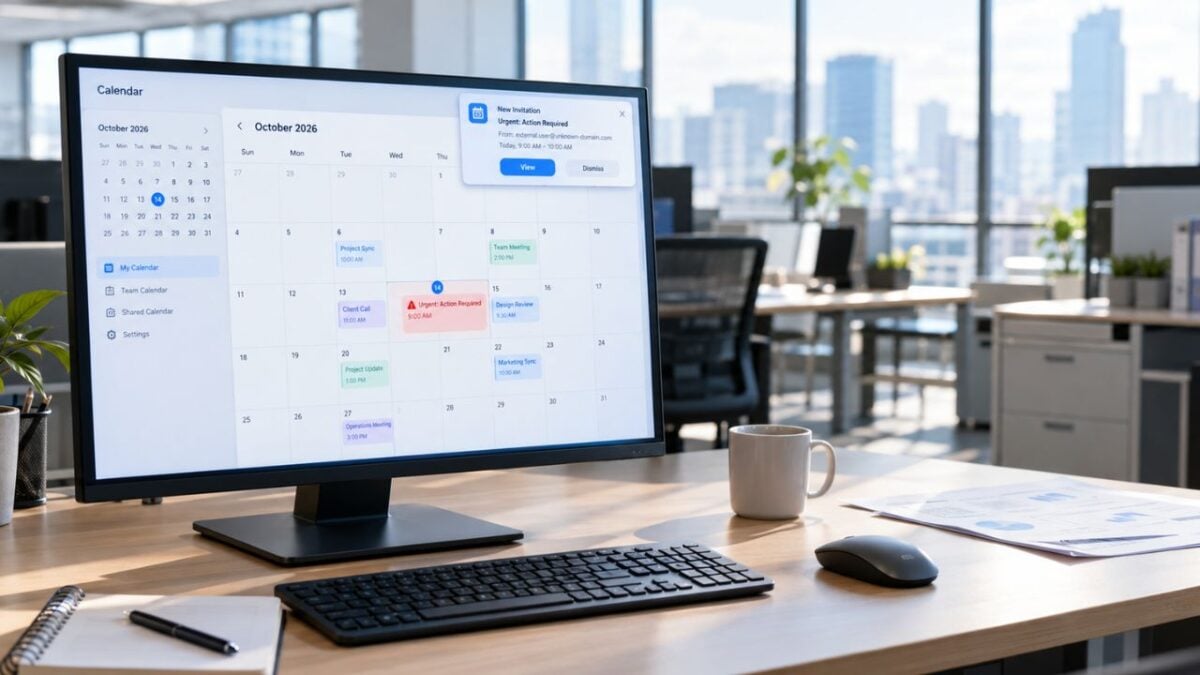
Criminals are now using fake meeting requests to reach workers directly through their calendars. Security researchers at Sublime warn that these “ICS phishing” attacks have grown quickly in recent months, and they are urging people to be cautious.
The con often begins with an unexpected meeting invite or a notice about a financial matter appearing on someone’s calendar. The invite might contain a bogus invoice or a QR code. Believing they overlooked the event, the person clicks a link and ends up on a fraudulent site that steals passwords or drops malware. Such pages commonly pose as Microsoft, Google, PayPal and other trusted brands.

Scammers deliver the same message to email and calendar together to improve their chances of being noticed. A spam filter may block the email, yet the calendar invite can still reach the user. The reason is that Google Calendar and Microsoft 365 process invitations in their own way, particularly when they are set to add events from emails automatically.
Sublime recorded a rise of about 33,000 percent in ICS phishing cases from May to September. Attacks doubled or tripled between May and June, then climbed by more than 1,000 percent each month after that. The approach is low cost, takes advantage of how calendars handle invites, and leans on the trust users place in Google and Microsoft.
People should be wary of messages that mention money or create a sense of urgency, especially from unknown senders. Experts advise against answering a suspicious invite, even to decline it, because a reply shows the account is active. Instead, delete it and report it as spam. If an invite from a known contact seems strange, verify it through a different channel.