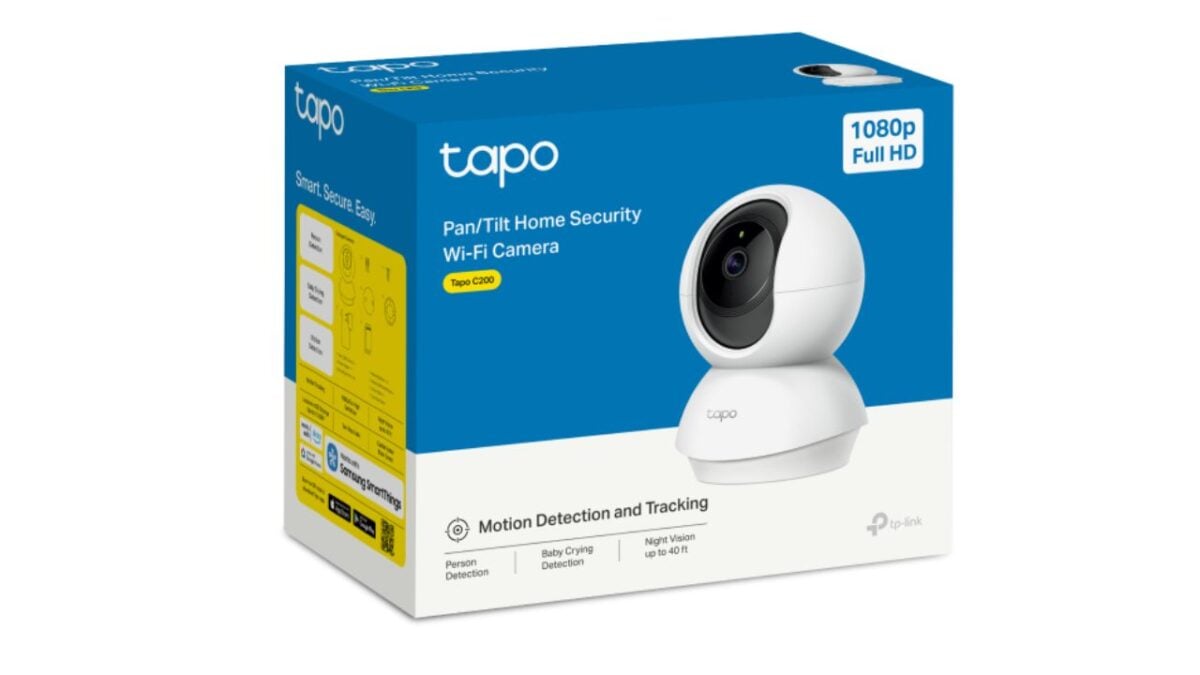

If you own a TP-Link Tapo C200 security camera, you might want to hear this.
Researchers from security firm OPSWAT have discovered serious vulnerabilities in the TP-Link Tapo C200, a consumer-grade Wi-Fi security camera commonly used for home security, monitoring pets and babies, and by small businesses.
One major flaw, tracked as CVE-2026-15315, has been rated as “high severity.” The vulnerability could allow hackers with network access to the camera to bypass its login system and gain administrator privileges without knowing the account password.
OPSWAT explained that the C200 uses a challenge-response system to verify that someone attempting to log in knows the camera’s password. However, previously transmitted information could be replaced and incorrectly accepted as valid authentication.
According to the researchers, once an attacker gains access to the network, they only need to send “a handful of malicious requests” that can take just a few minutes to gain access to the camera.
OPSWAT also discovered another vulnerability that could allow hackers to take full control of the camera and potentially use it to attack other devices on the same network. The researchers have not disclosed the details of this flaw as they are working with TP-Link to confirm and resolve the vulnerability.
A third vulnerability could allow attackers on the same network to send large amounts of traffic to the camera, causing its management service to crash. This could take the camera offline and prevent its owner from accessing it until the service recovers.
TP-Link has already released a security advisory and software update addressing the vulnerabilities. Owners are encouraged to update their cameras to the latest available software.